Armor Founder: AI Needs Governance, Not a Ban
Armor Founder and CEO Chris Drake urged for AI governance, not a ban, at GovWare 2026 in Singapore. He emphasized enabling automated business work within policy frameworks.
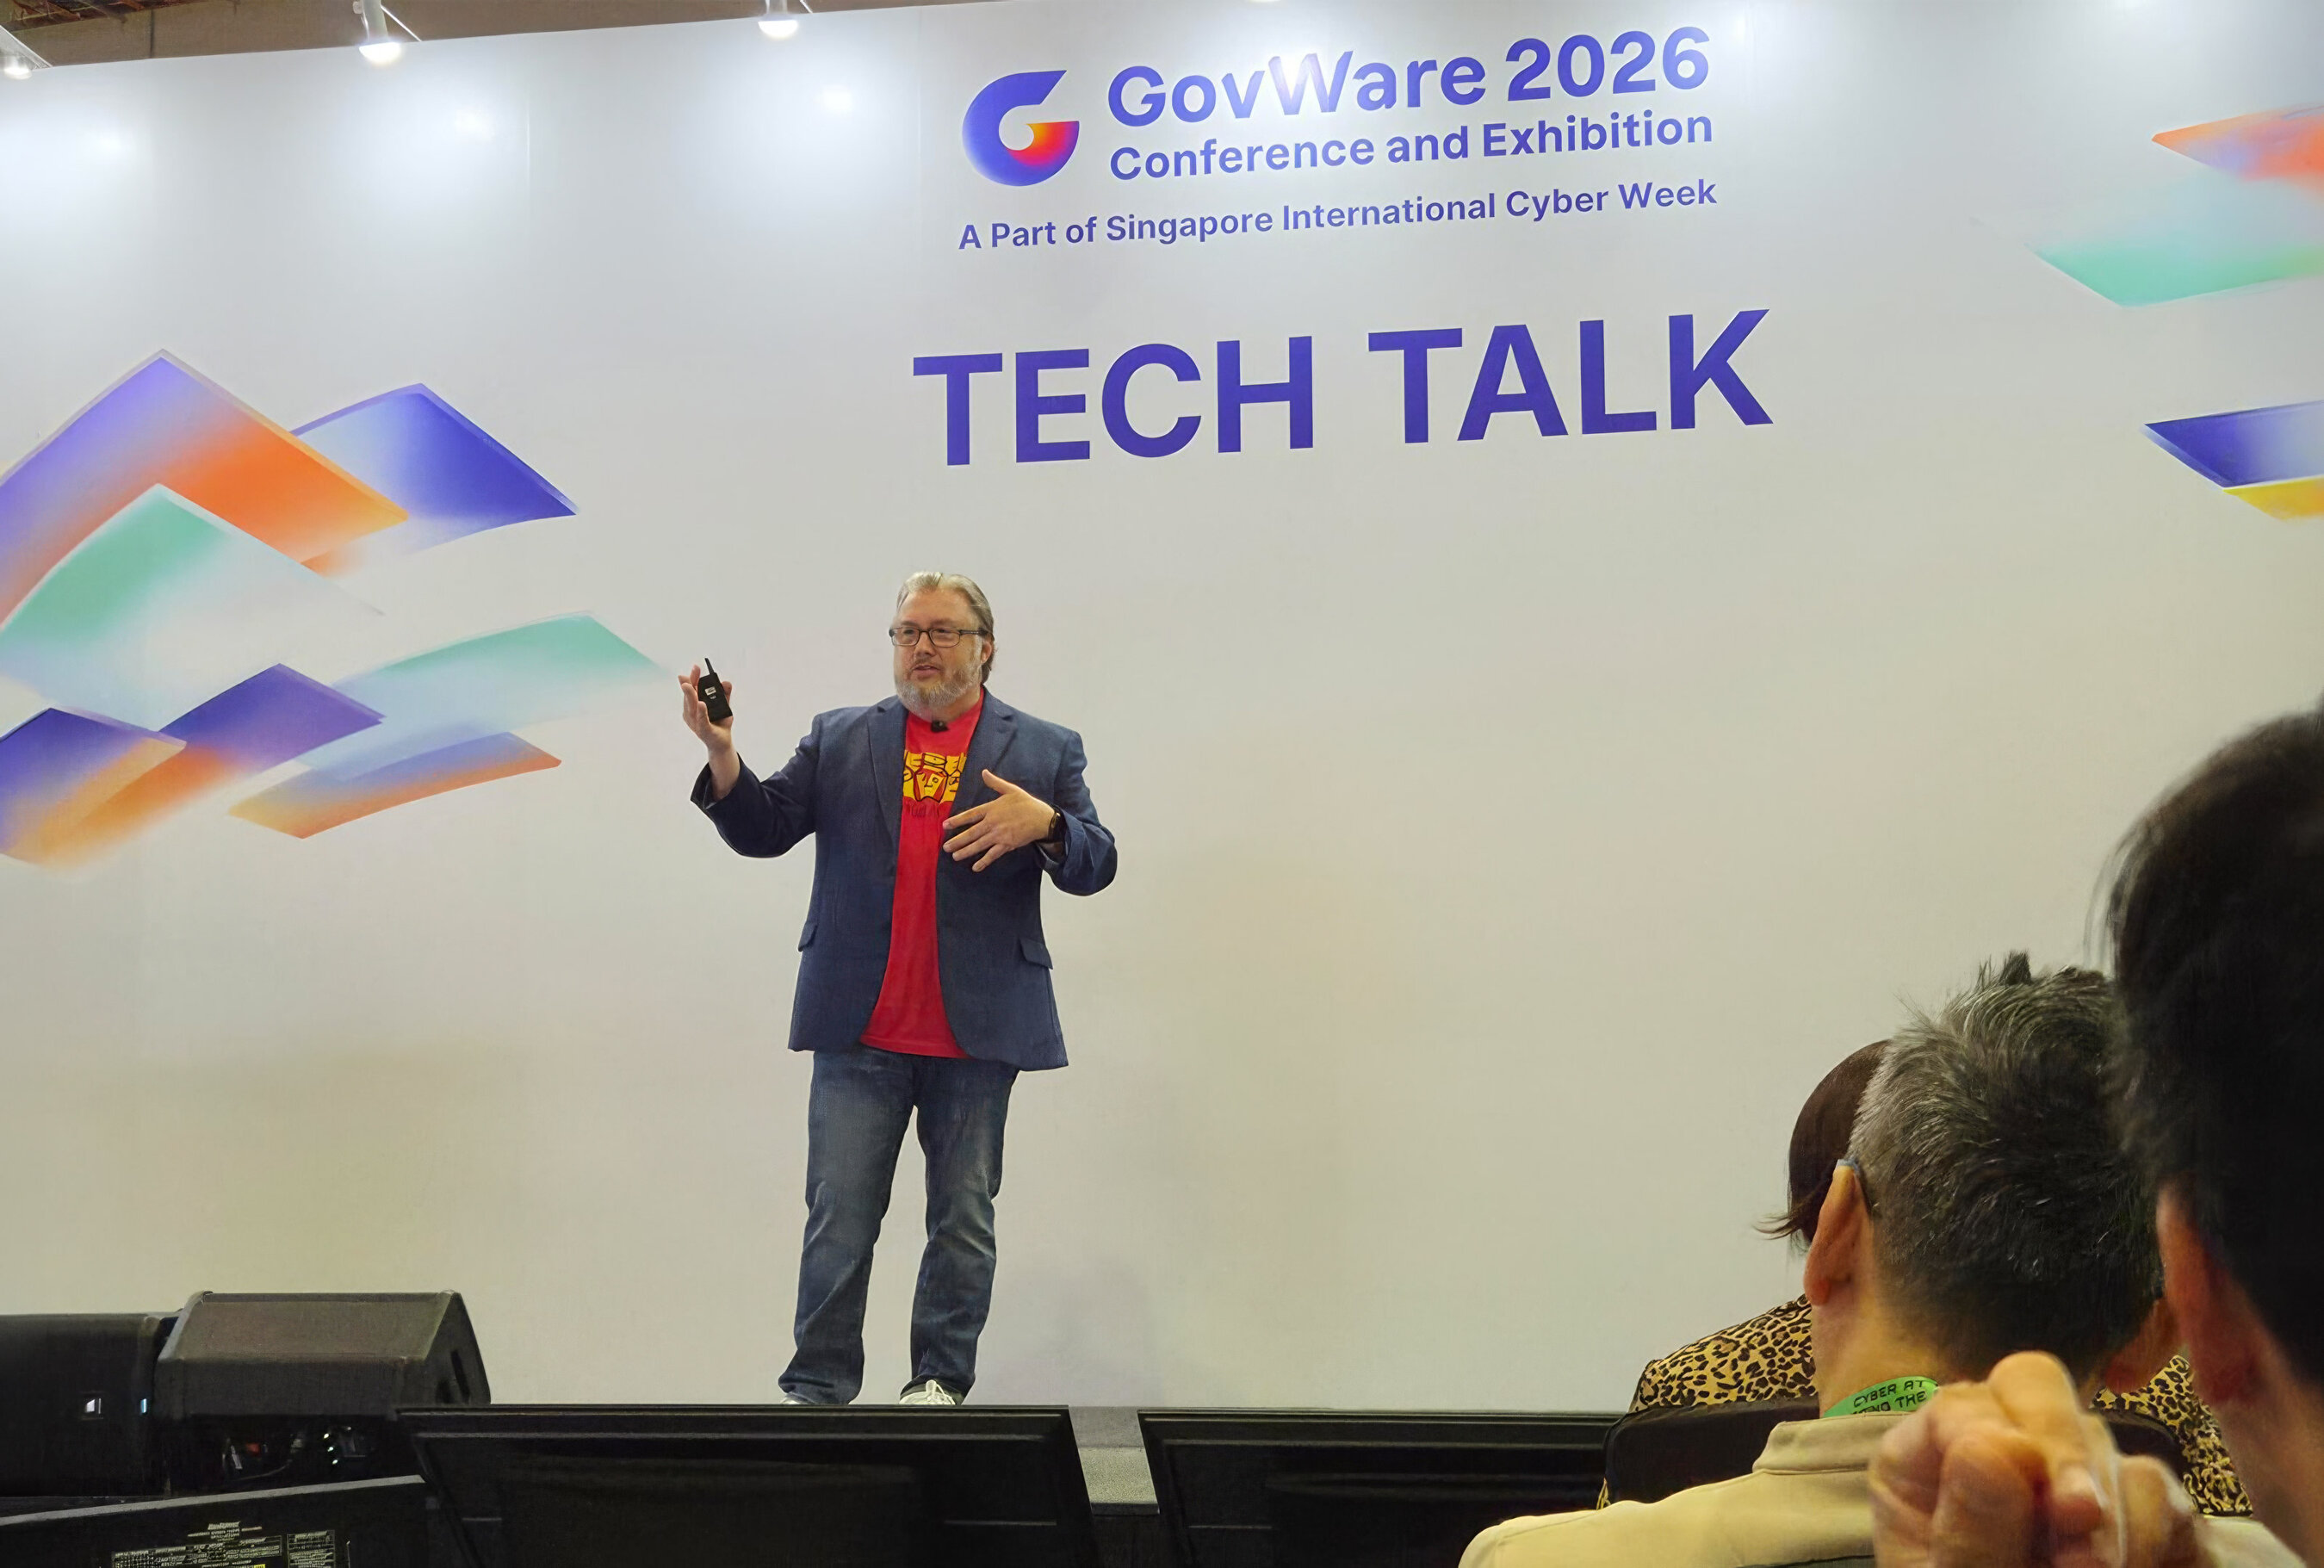
Armor Founder and CEO Chris Drake told attendees at GovWare 2026 in Singapore that artificial intelligence (AI) requires a path of governance, rather than an outright ban. Drake argued that Chief Information Security Officers (CISOs) must balance enabling AI innovation with protecting business operations. He noted that AI is already entering organizations through employees and their existing tools, often without a specific security decision.
Drake contrasted AI's arrival with the earlier cloud transition, when security teams could vet providers. AI, however, can embed itself into existing browsers and productivity tools without such checkpoints. He highlighted risks associated with visibility gaps in local virtual machines and isolated environments, where tools like Endpoint Detection and Response (EDR) may struggle to monitor activity.
Drake urged CISOs to obtain clear mandates to approve, restrict, or pause AI usage. He stressed the need for designated risk owners and clear escalation paths. As a solution, he proposed that organizations should first classify their data, own their routing policies, and demand auditable evidence. This would enable automated and secure AI utilization for business needs.
Armor, serving regulated industries since 2009, has developed its own governed AI platform, Sovereign AI, to securely handle customer data. Drake concluded by advising CISOs to ask three questions before granting AI tools access: What can it touch? Where can it send data? And where can it send commands?