Deutsche Telekom warns of sophisticated email phishing scheme
Deutsche Telekom has identified a two-stage phishing attack that leverages legitimate account recovery processes to deceive customers into clicking malicious links.
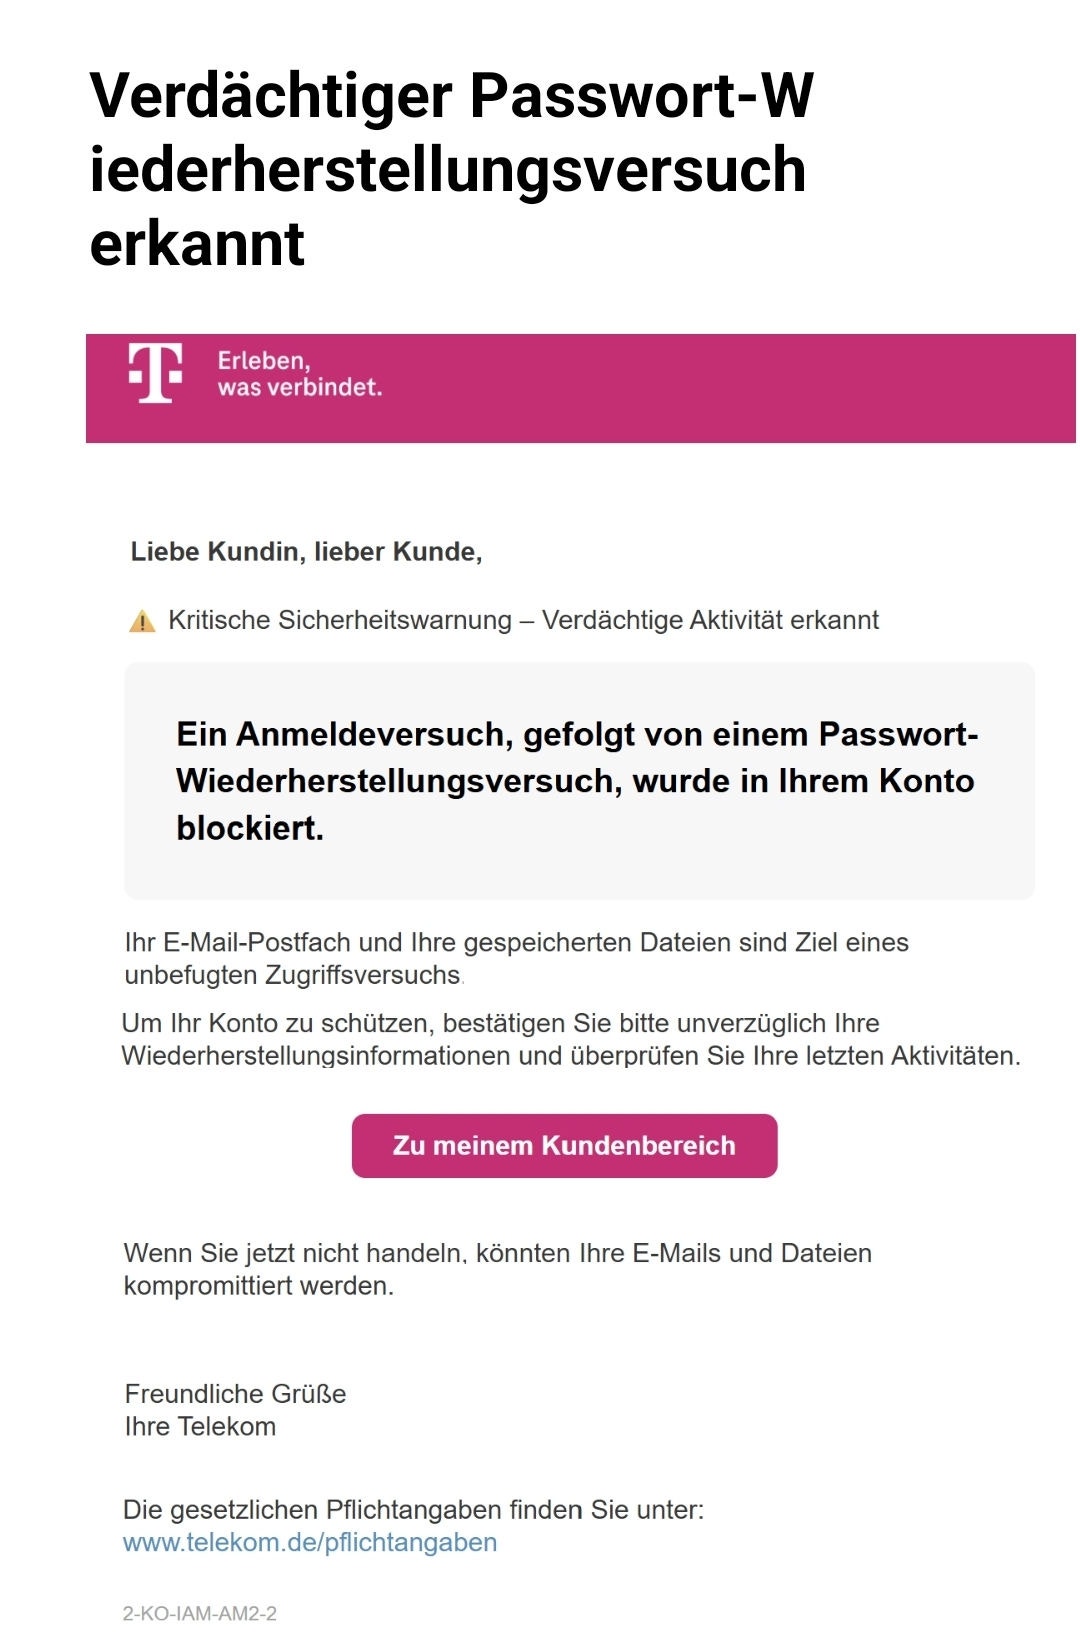
Deutsche Telekom is alerting customers to a recurring phishing campaign that utilizes both real and fraudulent emails to compromise accounts. The attackers initiate the scheme by triggering a legitimate system request for an account recovery code. This is followed by a deceptive email sent by the attackers themselves, which mimics an official security alert.
By manipulating sender headers, the attackers make the fraudulent emails appear to originate from legitimate Deutsche Telekom addresses. Recent variants of this scheme include claims that account recovery details have been modified, aiming to pressure victims into interacting with phishing links embedded in the message. These messages often incorporate fragments of the user's actual contact information to enhance their perceived authenticity.
Deutsche Telekom advises customers to ignore these messages and refrain from clicking any links provided within them. The company emphasizes that managing account security should only be conducted by navigating directly to the official customer portal in a browser, where users can manually update passwords or enable multi-factor authentication.